Cybersecurity researchers have uncovered a new Windows-based infostealer malware called VOLTA-AUTODOXER, which uses artificial intelligence to analyse stolen information and identify financially valuable victims. The discovery was reported by Cisco Talos researchers, who found that the malware combines traditional data theft with AI-powered victim profiling. Unlike ordinary infostealers that mainly collect passwords and personal information, VOLTA goes a step further by building a detailed profile of the infected computer’s owner. Its main objective is to help attackers understand which victims could offer the greatest financial benefit.
VOLTA collects a wide range of sensitive information from infected systems, including browser passwords, cookies, saved payment card details, cryptocurrency wallet information and Microsoft authentication tokens. It also targets active sessions from platforms such as Discord, Telegram, Steam and Roblox, along with email profiles, screenshots and other account-related information. The malware can access saved Wi-Fi passwords, SSH credentials and cloud service configuration files. This information gives attackers access to both personal and professional accounts, potentially exposing valuable digital assets.
After collecting the information, VOLTA searches deeper into the victim’s accounts to build a more complete picture of their identity and financial activities. It can examine Gmail messages for purchase receipts from services such as Amazon, DoorDash, Uber Eats, Walmart and PayPal. It also collects food delivery order histories and uses available account information to estimate the value of digital assets, including Roblox items. These details can help attackers identify a victim’s location, workplace, spending habits and other personal information that may be useful for targeted attacks.
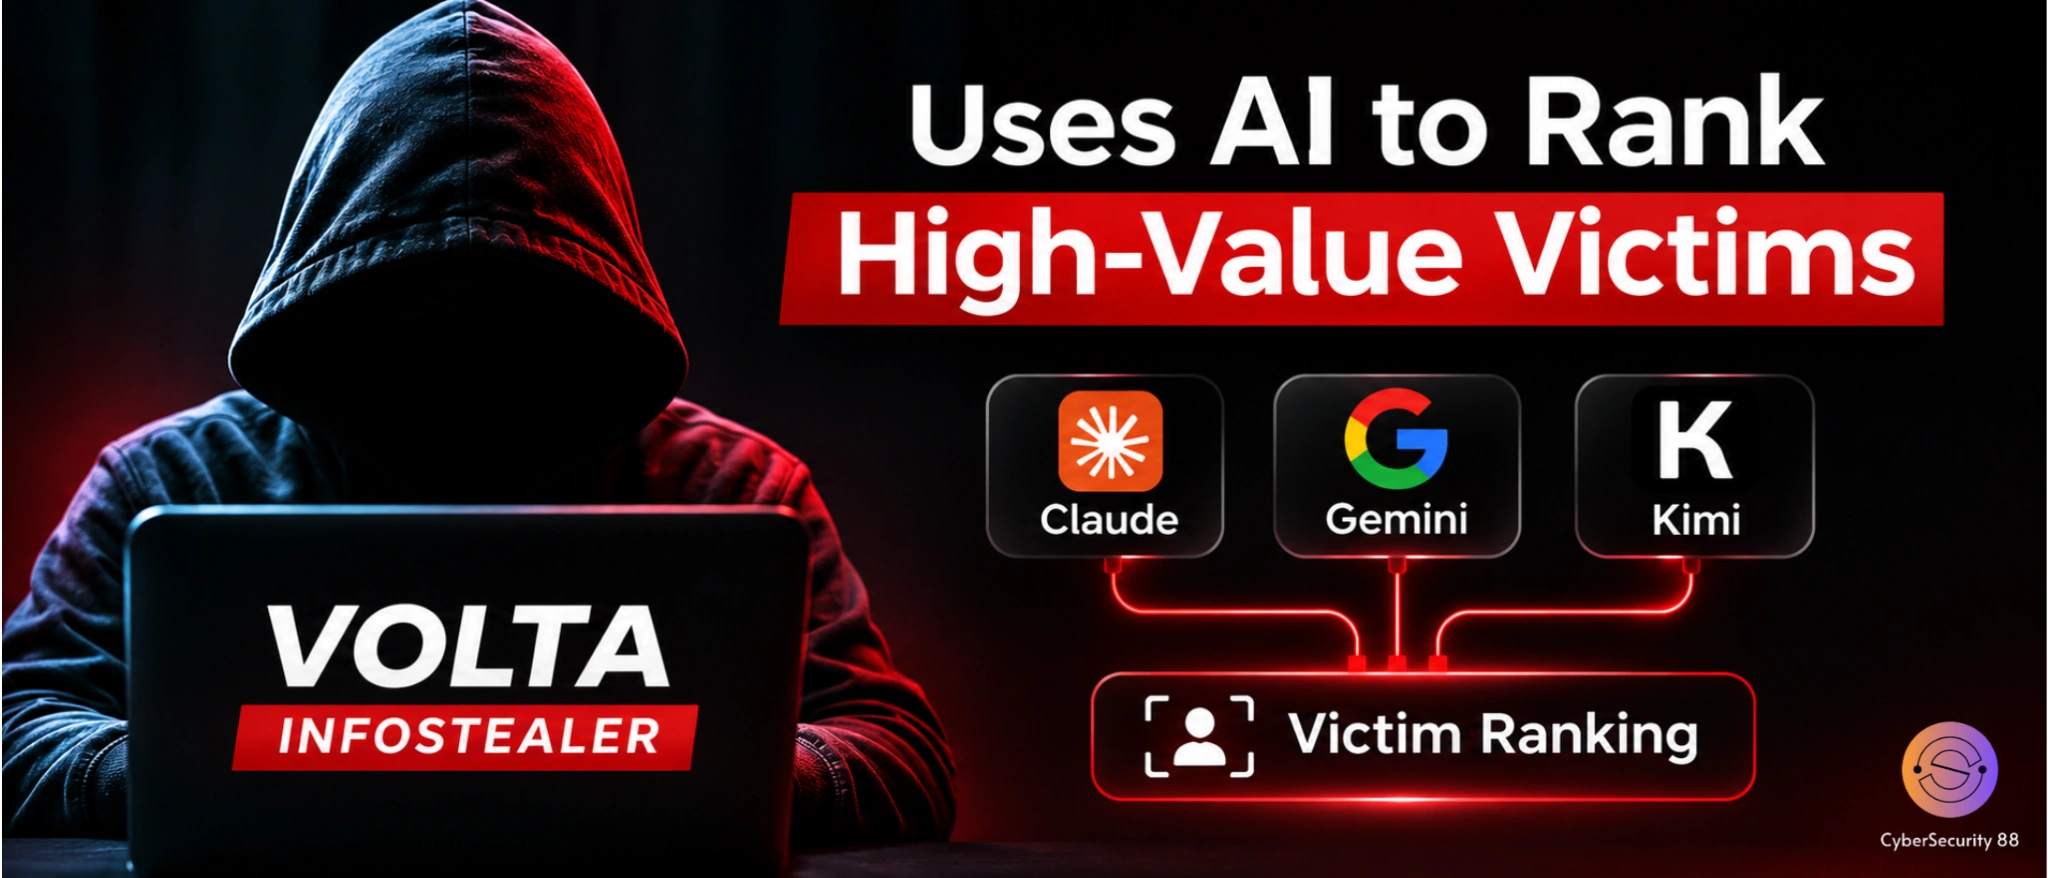
One of the most concerning features of VOLTA is its ability to use multiple AI models to analyse the stolen information. The malware sends the collected data through OpenRouter, an AI model gateway, and initially uses Anthropic’s Claude Opus 4.6 to prepare a detailed victim assessment. If Claude refuses the request or fails to provide a suitable response, VOLTA switches to Moonshot AI’s Kimi K2 and then Google’s Gemini 2.5 Flash. The AI is instructed to act like a forensic intelligence analyst and rank the victim’s assets according to their potential financial value.
The AI-generated assessment helps attackers understand which victims may be worth targeting first, reducing the time needed to manually examine stolen information. VOLTA prepares a structured report containing details about the victim’s identity, available assets and security practices before sending the collected information and analysis to the operator through Telegram. Researchers also found that the malware can continue operating even without its AI functionality, meaning the AI analysis is an additional feature rather than a requirement. Its design includes configurable settings, suggesting that the malware may have been developed for distribution to multiple cybercriminals.
Cisco Talos has not confirmed whether VOLTA-AUTODOXER has already been used in real-world attacks, but its discovery highlights a growing concern about the misuse of commercial AI tools in cybercrime. By combining traditional information theft with automated victim analysis, attackers can identify valuable targets more quickly and make better use of stolen credentials and authentication tokens. Security researchers warn that this development could make sophisticated targeting techniques accessible to less experienced cybercriminals. It also shows how artificial intelligence is becoming another tool that attackers can use to improve existing malware operations.
Stay alert, and keep your security measures updated!
Source: Follow cybersecurity88 on X and LinkedIn for the latest cybersecurity news