Cybersecurity researchers have uncovered a previously undocumented threat group known as Bronze Sandcastle, believed to be aligned with China. According to Sophos researchers, the group has been targeting organizations across Asia and Africa since mid-2025. Its activities were observed between August 2025 and August 2026, affecting victims in the Philippines, Taiwan, Afghanistan, Namibia, and possibly South Korea. Researchers also found signs that the group is most active in the UTC+8 time zone.
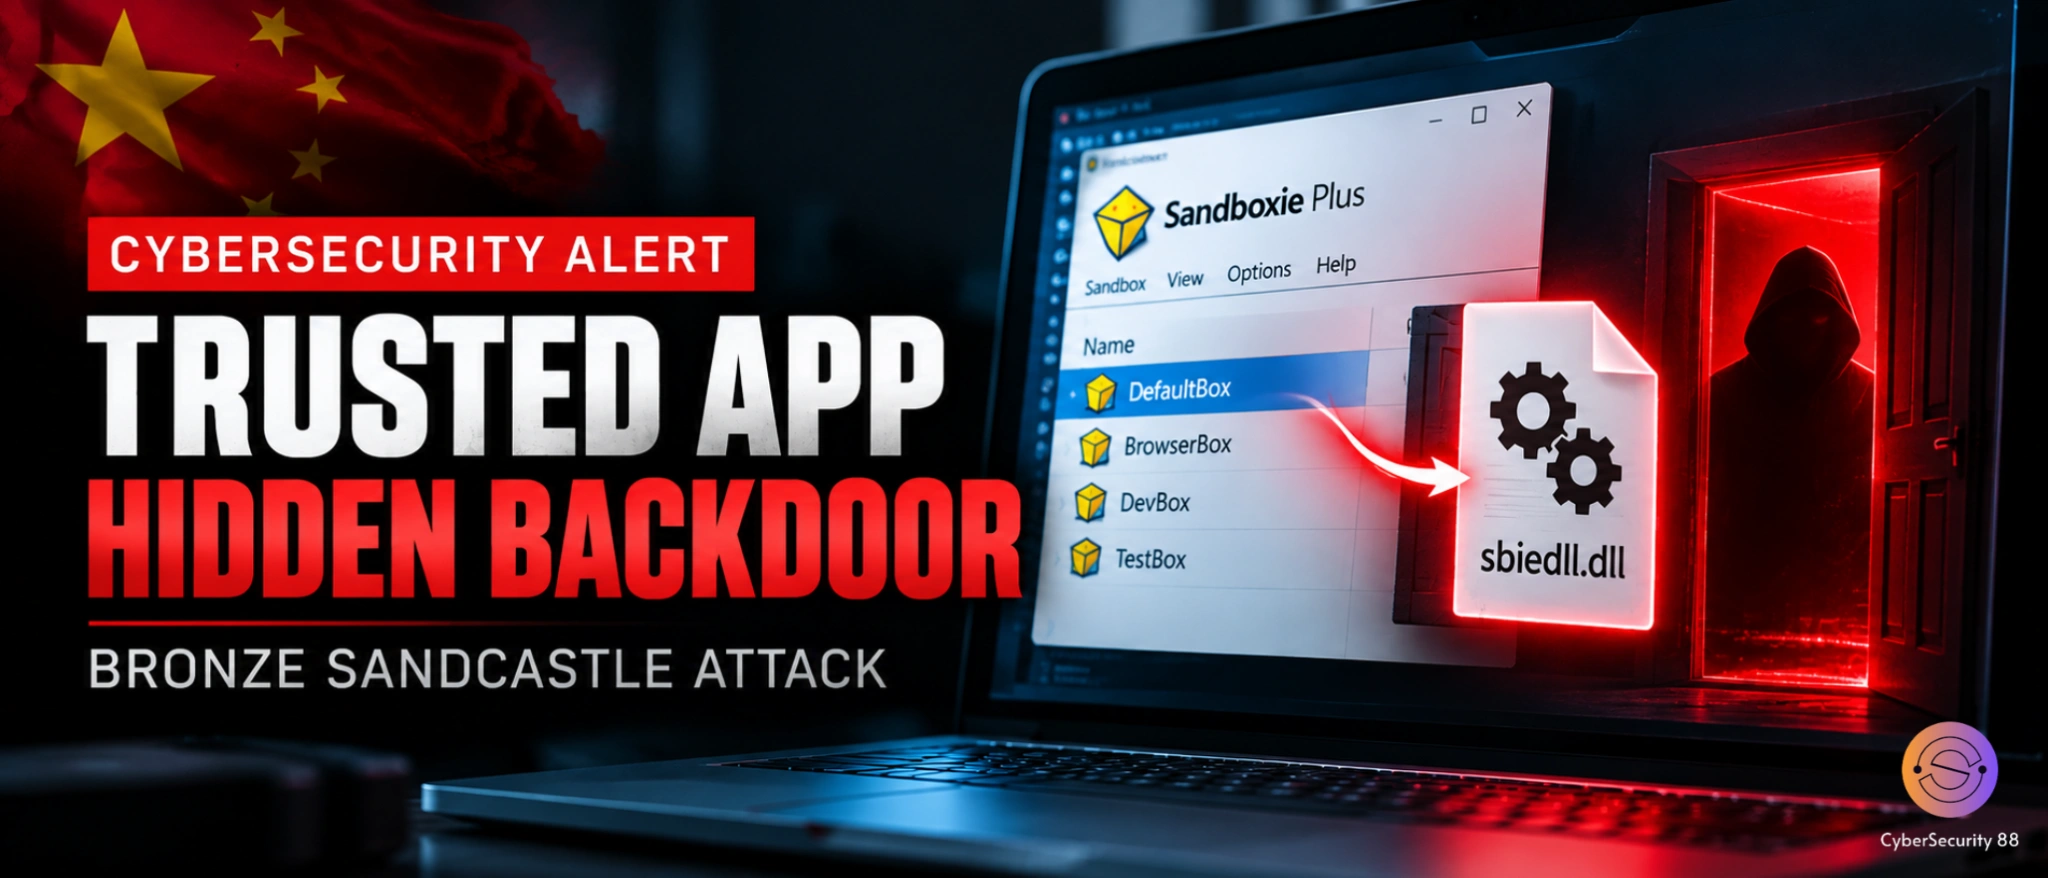
The group’s main technique involves DLL sideloading, a method that abuses how Windows loads Dynamic Link Libraries (DLLs). Attackers place a malicious DLL alongside a legitimate application, causing the program to load and execute the harmful file instead of the intended library. Bronze Sandcastle repeatedly used legitimate Sandboxie executables with a malicious file named sbiedll.dll. This allows malicious code to run through a trusted application, potentially making detection more difficult.
Researchers found that the group also used other legitimate applications to carry out similar attacks. These included Java, Krita, NVDA, LINE, and Microsoft Sysinternals utilities. The attackers paired these programs with specially named malicious DLL files to execute their code. In many cases, the DLLs loaded encrypted payloads stored in files named config.ini. This approach helps the attackers hide their activities and change their configurations without replacing the malicious DLLs.
The encrypted payloads contain backdoor functionality that allows attackers to collect information from compromised systems. Researchers identified two versions, numbered 1.1.5 and 1.1.7. These payloads can gather information about user accounts, local networks, system details, running processes, keystrokes, and screenshots. The malware executes its payload directly in memory, reducing the number of additional files left on disk and making traditional file-based detection more challenging for security tools.
The investigation also revealed that the malware communicated with external services to receive instructions and retrieve encrypted configuration files. Version 1.1.5 was observed contacting specific command-and-control domains, while version 1.1.7 used GitHub repositories to download encrypted configurations. Researchers also identified similarities between the payload and certain shellcode-loading techniques, although the malware was not considered a standard Metasploit artifact. These findings indicate that Bronze Sandcastle uses multiple methods to maintain access and collect information from compromised environments.
Sophos researchers recommend that organizations focus on suspicious behaviour rather than relying only on file-based detection. Security teams should investigate unusual DLL loading, applications reading encrypted local files before executing code in memory, and unexpected process activity. Monitoring network communications and suspicious account or system discovery commands can also help identify possible intrusions. The findings highlight how attackers can misuse trusted software to hide malicious activity, making continuous monitoring and endpoint security important for protecting organizational systems.
Stay alert, and keep your security measures updated!
Source: Follow cybersecurity88 on X and LinkedIn for the latest cybersecurity news