Blockchain investigator ZachXBT has revealed how he went undercover as a cryptocurrency client to infiltrate a Chinese organized-crime network that he says was involved in laundering more than $1 billion linked to multiple cryptocurrency exploits for North Korea’s Lazarus Group.
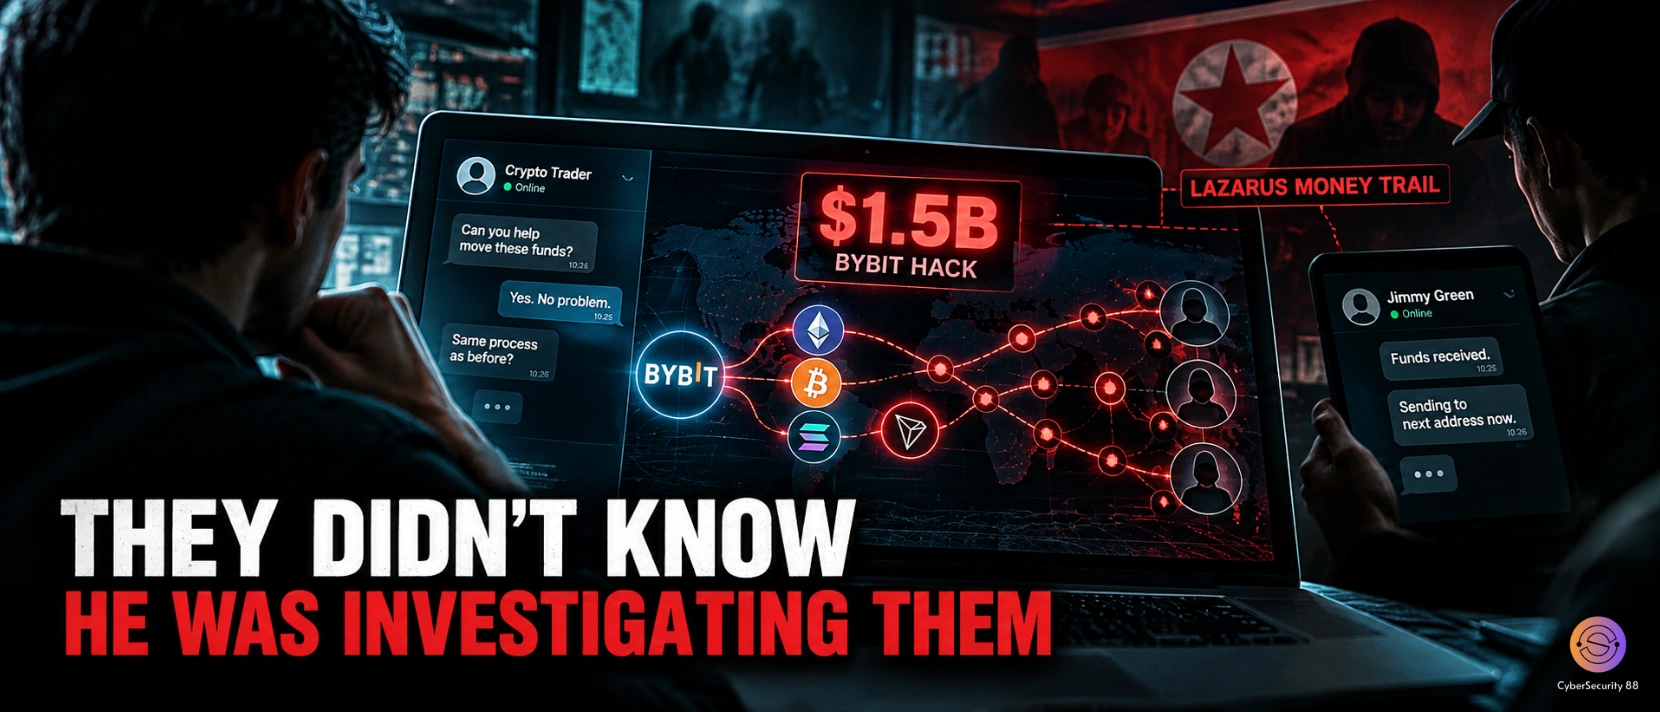
The investigation was connected to the February 2025 Bybit hack, in which approximately $1.5 billion worth of cryptocurrency was stolen. The FBI officially attributed the theft to North Korea and identified the activity as “TraderTraitor.” The bureau warned at the time that the stolen assets were being moved across thousands of addresses and multiple blockchains.
According to ZachXBT, he discovered more than 15 accounts in public Telegram and Discord groups that were looking for people to process transactions connected to the stolen Bybit funds. He eventually contacted an operator using the alias “Jimmy Green” and presented himself as a potential customer.
To gain the operator’s trust, ZachXBT said he carried out cryptocurrency transactions while accepting losses of around 5% on individual orders. He said he ultimately put up approximately $349,700 for the operation.
As the relationship developed, Jimmy Green allegedly began sharing cryptocurrency wallet addresses, screenshots and information about planned fund movements. ZachXBT compared those conversations with publicly available blockchain transactions to determine whether the claims matched actual activity.
One important connection involved a wallet that received transaction fees from an address linked to the Bybit theft. In another case, a screenshot sent by Jimmy Green showed a transaction that ZachXBT said matched a THORChain transaction in both timing and amount.
The investigation also identified a group of Solana addresses connected to more than $12 million in funds linked to the Bybit exploit. The funds were moved through several blockchain networks, including Bitcoin, Ethereum, Solana and Tron. Moving assets across different networks is one technique criminals can use to make tracing stolen cryptocurrency more difficult.
ZachXBT said the laundering network also used Uniswap liquidity pools involving low-liquidity tokens as part of its methods for moving the funds. In one significant result from the investigation, approximately 442,000 USDT connected to the identified wallet cluster was later frozen by Tether.
The investigation was not limited to the Bybit theft. ZachXBT said information provided by the operator also helped him trace other suspicious cryptocurrency movements. He connected a separate case involving approximately 332,000 USDC to funds from the 2023 Poloniex exploit. He also traced around $3 million in fraudulent proceeds discussed by the operator to a wallet associated with Huione Guarantee, a Cambodian network that later faced action from U.S. authorities.
ZachXBT said the information collected during the operation was shared with private-sector investigators and law-enforcement agencies working on the cases. He also said that, since 2022, his investigations have helped facilitate freezes involving more than $75 million connected to North Korea-related cryptocurrency incidents.
The identity of the person operating under the name “Jimmy Green” has not been publicly established by law enforcement. Likewise, the broader claim that the network laundered more than $1 billion remains an assessment from ZachXBT rather than a figure independently confirmed by authorities.
The disclosure highlights how blockchain investigations can combine undercover work with publicly visible transaction data. Even when stolen cryptocurrency moves through several blockchains and wallets, transaction amounts, timing and wallet connections can sometimes reveal links between apparently separate transfers.
The Bybit case remains one of the largest cryptocurrency thefts ever recorded. Bybit has continued working with investigators, exchanges and other organizations to trace and recover the stolen assets. The company said in August 2026 that approximately $48.4 million had been recovered and more than $30.5 million had been frozen across exchanges and custodians.
The latest investigation does not mean all of the stolen cryptocurrency has been recovered. Instead, it provides another detailed look at how laundering networks allegedly operate and how investigators can use blockchain records and undercover intelligence to identify and freeze illicit funds.
Stay alert, and keep your security measures updated!
Source: Follow cybersecurity88 on X and LinkedIn for the latest cybersecurity news