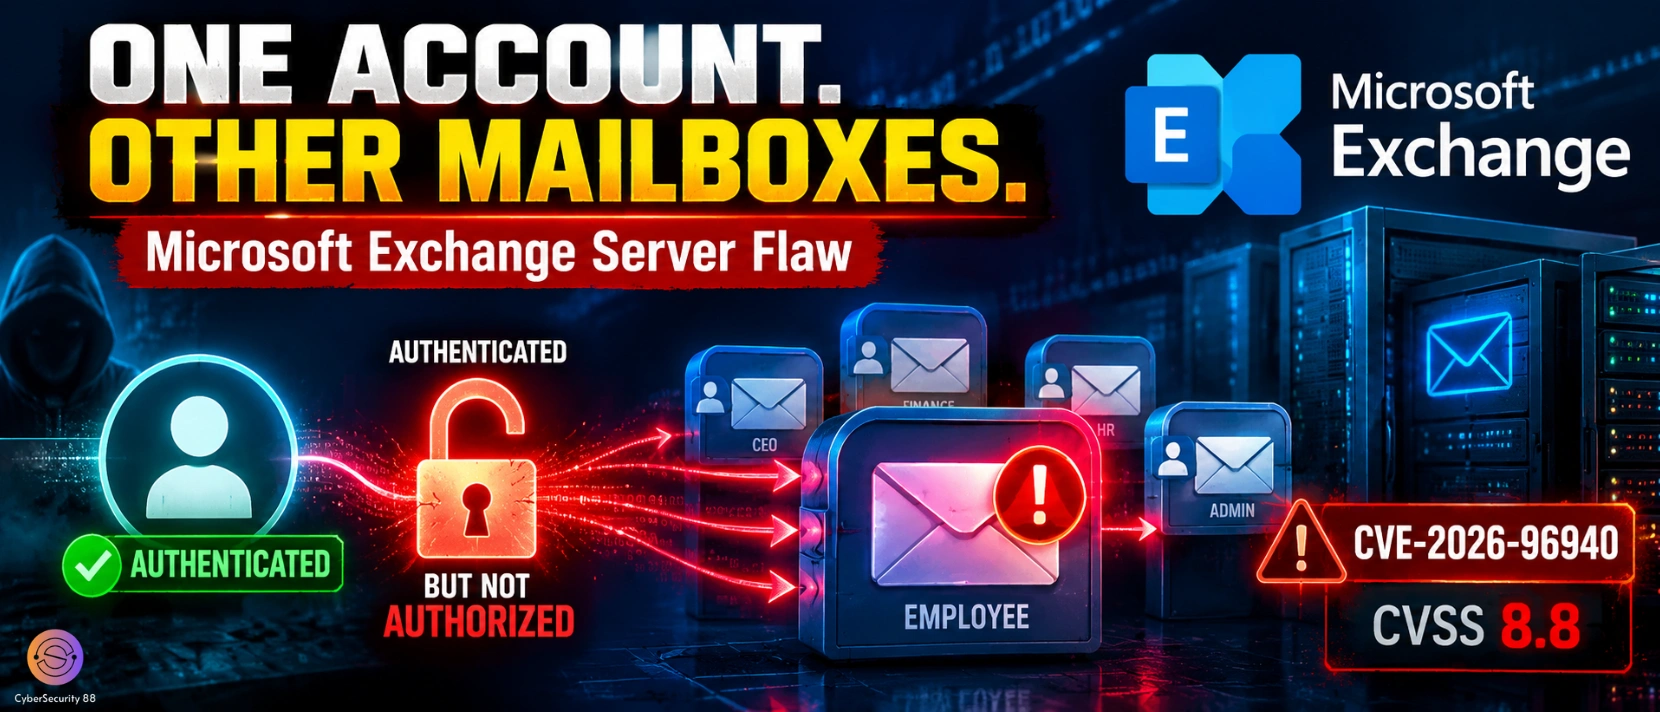
Microsoft has released an out-of-band security update for a high-severity vulnerability in Exchange Server that could allow an authenticated attacker to access other users’ mailboxes. The vulnerability is tracked as CVE-2026-96940 and was disclosed by Microsoft on October 2, 2026. It has a CVSS score of 8.8 out of 10, making it a serious security issue for organizations running affected Exchange servers. The flaw is caused by weak authorization controls that can allow an attacker with valid authentication to gain higher privileges over a network.
In simple terms, an attacker who already has authenticated access could abuse the flaw to reach mailboxes belonging to other users in the same organization. If successfully exploited, the attacker could read email messages and attachments that they should not normally be allowed to access. Microsoft classifies the issue as an elevation-of-privilege vulnerability, and exploitation does not require another user to interact with the attack. However, the flaw does not allow attackers to cross tenant boundaries and access mailboxes belonging to another organization.
The vulnerability affects several on-premises versions of Microsoft Exchange Server. These include Exchange Server Subscription Edition RTM, Exchange Server 2019 CU14, Exchange Server 2019 CU15 and Exchange Server 2016 CU23. Microsoft has released the required protection through its September 2026 V2 security updates, which add the fix for CVE-2026-96940. Organizations running Exchange 2016 or Exchange 2019 should also be aware that these versions have reached end of support, so security updates are currently available through Microsoft’s Period 2 Extended Security Update program.
Microsoft’s September 2026 V2 release is important because organizations that installed the earlier September update should not assume that this particular vulnerability was already fixed. The new packages contain the protection specifically addressing CVE-2026-96940, with separate updates provided for the affected Exchange versions. For example, Microsoft lists KB5129955 for Exchange Server Subscription Edition RTM and KB5129957 for Exchange Server 2019 CU14. Administrators need to select the update that matches the Exchange version and cumulative update running in their environment.
Exchange Online customers are in a different position because Microsoft has already deployed a related service-side fix for the cloud service. As a result, organizations using Exchange Online do not need to take additional action specifically for this vulnerability. However, companies operating hybrid environments should not assume that their on-premises Exchange servers are automatically protected. Microsoft recommends applying the applicable security update to on-premises Exchange servers and systems running the Exchange Management Tools as well.
At the time of disclosure, Microsoft said it was not aware of active exploitation of CVE-2026-96940. There is also no reported evidence that the vulnerability has been weaponized in the wild, but Microsoft has rated its exploitability as “Exploitation More Likely.” This assessment means organizations should not wait for attacks to appear before taking action, especially because the flaw can provide access to sensitive mailbox information. The vulnerability is therefore considered a serious patching priority for organizations using affected on-premises Exchange servers.
The issue is particularly concerning because business email accounts can contain highly sensitive information, including confidential conversations, documents, customer information and other internal communications. An attacker who can access another employee’s mailbox could potentially obtain information that was never intended for them. The risk becomes greater when an attacker can use one authenticated account to reach information belonging to other users. For organizations managing their own Exchange infrastructure, this makes applying the security update an important part of protecting internal email data.
Microsoft recommends that administrators apply the September 2026 V2 security updates as soon as possible and use the Exchange Server Health Checker to identify missing updates or other required actions. After installing the update, administrators should restart the affected server and confirm that Exchange services are working correctly. Microsoft also notes that Exchange security updates are cumulative, so organizations running a supported cumulative update do not need to install every previous security update one by one. For affected on-premises deployments, the main takeaway is clear: check the Exchange environment, install the correct V2 update and do not assume that the original September update included this newly addressed flaw.
Stay alert, and keep your security measures updated!
Source: Follow cybersecurity88 on X and LinkedIn for the latest cybersecurity news