Home icon Chevron Categories Chevron Blog Chevron News Chevron

WordPress Theme Vulnerability Under Active Exploitation, Allowing Full Site Takeovers

WordPress Theme Vulnerability Under Active Exploitation, Allowing Full Site Takeovers

July 31, 2025


A severe security flaw in the popular Alone – Charity Multipurpose Non-profit WordPress Theme is currently being exploited by malicious actors to compromise WordPress sites through unauthorized plugin installations.

Identified as CVE-2025-5394 and rated 9.8 on the CVSS scale, the flaw was discovered by security researcher Thái An. It impacts all theme versions up to 7.8.3 and has been patched in version 7.8.5, released on June 16, 2025.
According to Wordfence, the issue lies within the alone_import_pack_install_plugin() function, which fails to verify user capabilities. This oversight allows unauthenticated users to trigger remote plugin installations via AJAX, opening the door to arbitrary file uploads and remote code execution (RCE).

“This vulnerability lets attackers upload and execute arbitrary files without authentication—resulting in full control over the affected site,” said István Márton from Wordfence.

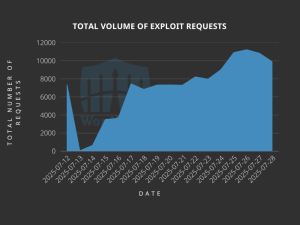
Attack attempts have been tracked back to July 12, suggesting the attackers may have been monitoring theme updates to exploit vulnerabilities before public disclosure.

To date, over 120,000 exploit attempts have been blocked, with activity traced to several IP addresses, including:

193.84.71.244, 87.120.92.24, 146.19.213.18, 185.159.158.108,
188.215.235.94, 146.70.10.25, 74.118.126.111, 62.133.47.18,
198.145.157.102, and 2a0b:4141:820:752::2

In these attacks, hackers often upload ZIP files (like wp-classic-editor.zip or background-image-cropper.zip) containing PHP-based backdoors. These allow remote command execution, upload of malicious files, and creation of rogue admin accounts using stealthy file managers.

Recommended Actions:
Website administrators using this theme should immediately update to the latest version, investigate any suspicious admin accounts, and review logs for signs of exploitation—particularly requests to:
/wp-admin/admin-ajax.php?action=alone_import_pack_install_plugin.

Stay alert, and keep your security measures updated!

Follow cybersecurity88 on X and LinkedIn for the latest cybersecurity news


Did you like the post? Share it in your media

Latest Articles

Featured

Hirudo Android Trojan Bypasses Banking App Security to Steal User Data

October 14, 2026 · Chetna Sehgal

Cybersecurity researchers have uncovered a new Android banking trojan called Hirudo that targets ...

Read More >
Featured

Researchers Use OpenAI AI Model to Build $250,000 Chrome Exploit in Just 6 Days

October 14, 2026 · Chetna Sehgal

Cybersecurity researchers at XBOW have developed a powerful exploit targeting Google Chrome on Wi...

Read More >
Featured

Daiichi Kosho Data Breach: 8.72 Million Records Potentially Exposed

October 12, 2026 · Chetna Sehgal

Japan’s major karaoke company Daiichi Kosho has disclosed a cybersecurity incident that may hav...

Read More >
Featured

CyberXero Uses Claude Code and 51 AI Agents to Steal 628,000+ Ukrainian Records

October 12, 2026 · Chetna Sehgal

A cybercriminal group known as CyberXero reportedly used artificial intelligence (AI) tools along...

Read More >
Featured

SonicWall SMA1000 Critical Vulnerability Exploited in Real-World Attacks

October 09, 2026 · Chetna Sehgal

SonicWall has warned that attackers are exploiting serious security vulnerabilities in its SMA100...

Read More >
Featured

Anthropic Launches Cyber Mission to Protect Critical Infrastructure and Open-Source Software

October 09, 2026 · Chetna Sehgal

Anthropic has announced the Anthropic Cyber Mission, a long-term initiative aimed at strengthenin...

Read More >
Newsletter line