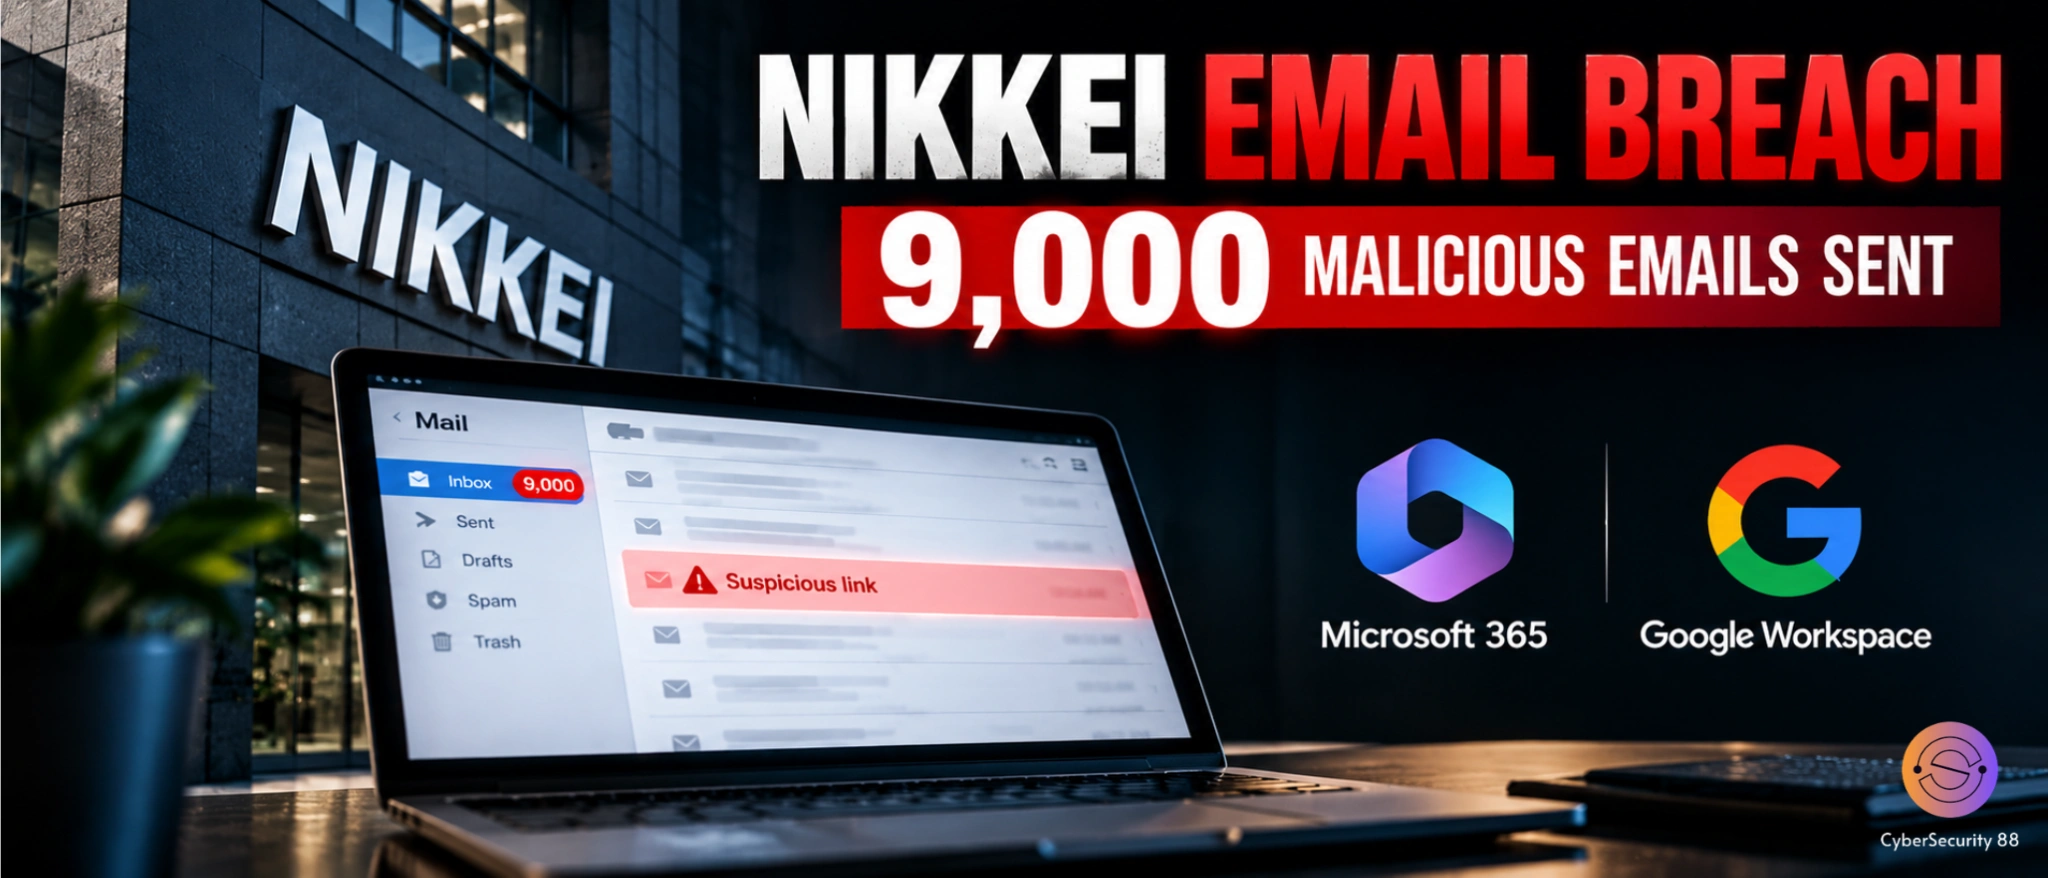
Japanese media company Nikkei has disclosed two separate security incidents involving employee email accounts on Microsoft 365 and Google Workspace. The company revealed the incidents on October 4, 2026, after unauthorized access was detected. The two incidents involved different employee accounts and Nikkei has not said that they were connected. No specific hacker or hacking group has been linked to either incident so far.
In the Microsoft 365 incident, an employee’s account was accessed by an unauthorized third party. On September 30, the compromised account was used to send around 9,000 emails to people inside and outside Nikkei. The messages were sent to employees as well as several people who had previously communicated with Nikkei staff. The emails contained links that directed recipients to malicious websites.
Nikkei said the incident may have exposed the names and email addresses of some recipients, along with parts of email conversations. The company changed the password of the affected account and said no further unauthorized logins have been detected since then. Nikkei also contacted recipients individually and asked them to delete the suspicious messages. The company reported the incident to Japan’s Personal Information Protection Commission.
The company also revealed a separate incident involving a Google Workspace account used by another employee. According to Nikkei, the account had been accessed without authorization from late July 2026. Google notified the company about the activity in early August, after which Nikkei changed the account password. The company said it has not detected any further unauthorized logins after taking that action.
The Google Workspace incident may have exposed personal information belonging to 1,646 employees and business partners. The potentially affected information includes names and email addresses. Nikkei said the information did not include data related to its readers or journalistic sources, and it has found no evidence that the exposed information has been misused so far. The company is continuing to investigate the full scope of both incidents.
Nikkei has warned employees, business partners and other contacts to be careful about suspicious messages that may appear to come from the company or its group companies. The incidents show how a single compromised employee account can be used to reach a large number of trusted contacts through phishing emails. Nikkei said it is taking the incidents seriously and will continue strengthening its security measures and information management practices.
Stay alert, and keep your security measures updated!
Source: Follow cybersecurity88 on X and LinkedIn for the latest cybersecurity news